
Featured Extensions
2026-09-24
2026-09-23
2026-09-23
2026-09-22
 EasyCommerce 1.4Eshop pro 5.8GDPR 2.27EasyForms 1.4OL No Right Click 4.2.7GPS Tools 7.6.1WP Funnels Pro 2.10.4
 Overview

 Joomla ExtensionsAccess & SecurityAdministrationAds & AffiliatesAuthoring & ContentCalendars & EventsClients & Communitieschats and ForumsContacts & FeedbackContent SharingCore EnhancementsDirectory & DocumentationStyle & DesignSite Managemente-CommerceEditorsFinancialHosting & ServersLanguagesLivingMaps & WeatherMarketingMigration & ConversionMiscellaneousSearch & IndexingMobileMultimediaStructure & NavigationNews DisplayBooking & ReservationsReal Estate and jobsPhotos & SlideshowSocial WebExtension SpecificSports & GamesToolsNewsletterSeo & metadataContent ConstructionformsPopups & iFramesBackupHelp Desk And SupportpollsData Import & ExportTable and listLogin/RegisterMenu SystemsUser & ProfileportfolioTabsRss FeedDatabase Managementdate and timePayments Site Analyticsjoomshoppingk2 extensionsAltaUserPointsVirtueMartHikaShopj2storeDJClassifieds Digicom ExtensionsJoomla TemplatessmartaddonsjoomshaperJoomDev templatesLthemeOrdaSoft Templatesinspirethemevinagecko templatesthemeforestyoothemeShape5Template monsterJoomlashine(JSN) TemplatesRsjoomlaRocket ThemeHOTthemeswarpthemejoomlarthtml templateGavickProBowthemejoomla51bestaddonjoomlabuffJoomla MonsterCmsboldjoomdonationJoomlabambooThemexpertjoomlaplateExtensions for joomlastackideasNooTheme9themestoretemplazamixwebtemplatesagethemesDj-extensionsJoomLeadVirtuemart TemplatesMobile JoomlaUnitemplatesJoomlaschoolWordpress PluginsWP Admin ToolsWP AdvertisingWP BackupWP Popup And IframeWP Calendars & eventWP Coming SoonWP Directory & ListingsWP E-Mail & NewslettersWP FormsWP ForumsWP Photo & GalleriesWP Help Desk – Live ChatWP Import & ExportWP Interface ElementsWP LMSWP Maps & WeatherWP MultiMediaWP User & ProfileWP Menu DesignWP MarketingWP language and speechWP news DisplayWP Page BuilderWP PaymentWp Access & SecurityWP SEO & OptimizeWP sports and GamesWP SliderWP Social Media PluginsWP UtilitiesWP shopWP Login And Registerwp Booking & Reservations wp Search and FiltersEDD PluginsWP file and downloadswp contact & feedbackWP Table and listWP Style & DesignWooCommerce Pluginswordpress Themeswp Blog templateswp BuddyPress templateswp Business templateswp Corporate templateswp Creative templateswp Directory & Listings templateswp eCommerce templateswp Education templateswp Miscellaneous templateswp Mobile templateswp Multi Vendor templateswp Multipurpose templateswp Newspaper – Magazine templateswpReal Estate templateswp Technology templateswp Restaurant templatesMagento ExtensionsPrestashop modulesPrestashop TemplatesSoftwaresLearningother ScriptsMobileApp And Source CodesWeb design & Graphics ToolsFree Downloadfontsshopify TemplatesAI Tools Joompaid AntiSpam – Zero-CAPTCHA Honeypot Spam Protection for Joomla 5 & 6


Form spam and automated bot submissions are persistent challenges for Joomla website administrators. Traditional defenses like Google reCAPTCHA, Cloudflare Turnstile, or puzzle-based captchas often frustrate genuine visitors, hurt conversion rates, and add external tracking scripts that degrade page loading speeds.
Joompaid AntiSpam eliminates form spam on Joomla 5 and Joomla 6 using invisible honeypot technology and behavioral time-trap validation—keeping your site 100% bot-free without requiring visitors to solve a single puzzle.
Rather than burdening legitimate users with interactive verification tests, Joompaid AntiSpam operates silently beneath the surface using a dual-layer defense mechanism:
Invisible Dynamic Honeypot Trap
The plugin injects hidden input fields into every form across your site using optimized client-side scripts. Human visitors cannot see or interact with these fields, but automated spam scripts and headless scrapers automatically detect and fill them. If the hidden field contains any data upon submission, the request is instantly rejected with a 403 Forbidden response.
Behavioral Time-Trap Validation
Automated bots typically complete and submit forms in fractions of a second. Human users require at least a few seconds to read, type, and click. Joompaid AntiSpam measures the elapsed submission time via an encoded timestamp token, instantly stopping submissions completed faster than natural human limits.
Zero-Friction User Experience (No CAPTCHA): Eliminates image puzzles, distorted characters, and "I am not a robot" checkboxes, keeping user engagement and checkout conversion rates high.
Native Joomla 5 & Joomla 6 Architecture: Built from the ground up utilizing Joomla’s modern service container (services/provider.php) and WebAssetManager. Fully compatible with PHP 8.1+ with zero dependency on the legacy Backward Compatibility plugin.
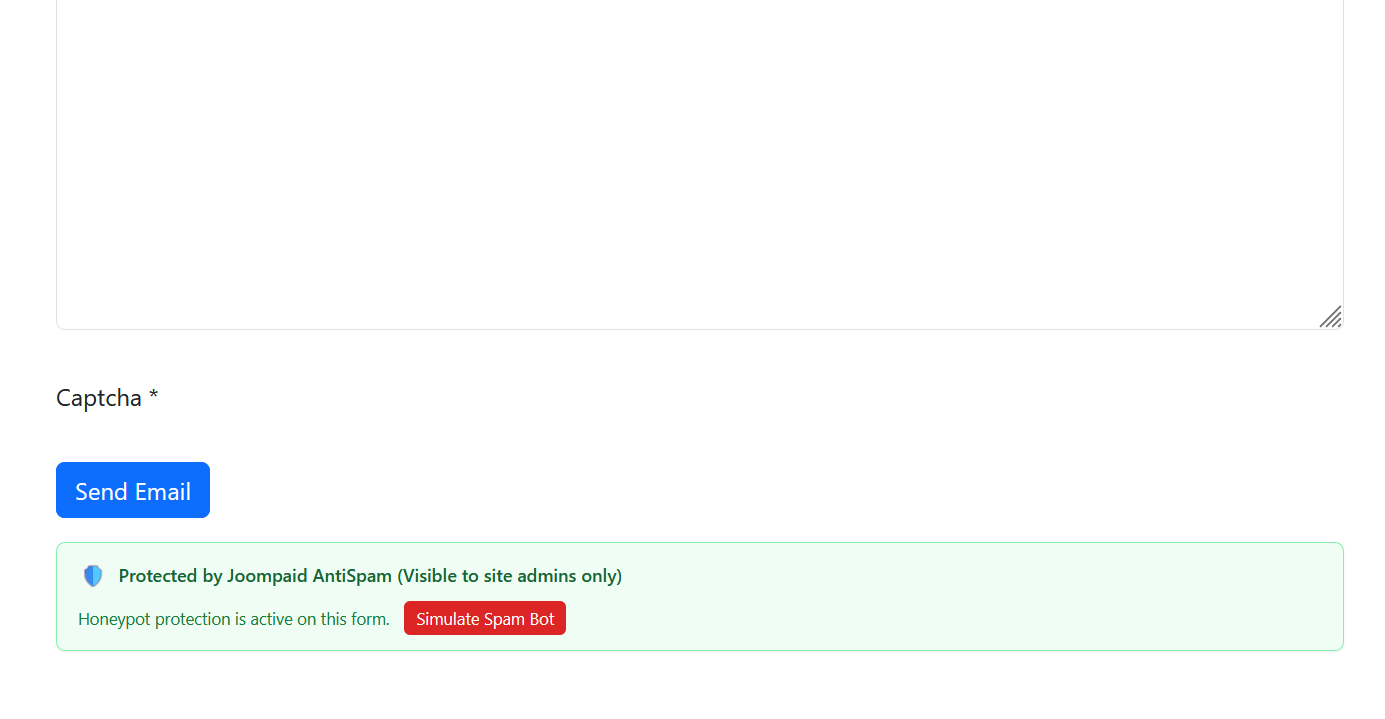
Exclusive Admin Verification Badge: Logged-in administrators see a subtle green security badge below active forms, confirming that protection is live without exposing any indicator to visitors or bots.
Integrated "Simulate Spam Bot" Test Tool: Administrators can click a built-in test button directly inside the badge to trigger the honeypot and verify the 403 Forbidden barrier in real time.
Universal Compatibility: Protects Joomla core contact forms, user registration and login forms, native comment modules, and third-party form builders such as RSForm! Pro and Convert Forms.
Asynchronous & Dynamic Form Detection: Uses a live MutationObserver to ensure forms loaded via AJAX, modal popups, and multi-step wizards are protected immediately upon rendering.
Speed & Privacy Focused (GDPR Compliant): Requires zero external API calls, tracking cookies, or third-party DNS lookups, ensuring maximum site performance and complete regulatory compliance.
Download the joompaid_antispam.zip extension archive.
Navigate to your Joomla Administrator dashboard: System > Install > Extensions.
Upload and install the package.
Go to System > Manage > Plugins, search for System - Joompaid AntiSpam, and toggle it to Enabled.
Open any front-end page with a form while logged into your admin session to view the active green protection badge and run test submissions.
Simulate Bot Button: Log in as an admin, click the red "Simulate Spam Bot" button under the form, and submit; you should see an immediate 403 Forbidden block.
Inspect Element Test: Press F12, locate the hidden joompaid_hp_check field, enter any text into it, and submit the form; the submission will be blocked instantly.
Real User Test: Open the form in an Incognito tab, fill it out naturally, and submit; the form must go through smoothly with zero CAPTCHAs or errors.
